

You can gain experience in cybersecurity without yet working in the sector. Building practical and demonstrable projects: your own lab, a security audit of an environment you control, challenges on practice platforms, and a portfolio to document your work. It doesn't replace work experience, but it demonstrates methodology and sound judgment, precisely what's sought after in a junior profile.
If you're just starting out, this probably sounds familiar: "junior" job postings require prior experience, and to gain that experience, someone has to give you your first opportunity. In this article, we explain how to break that cycle with five concrete actions and a 30-day plan.
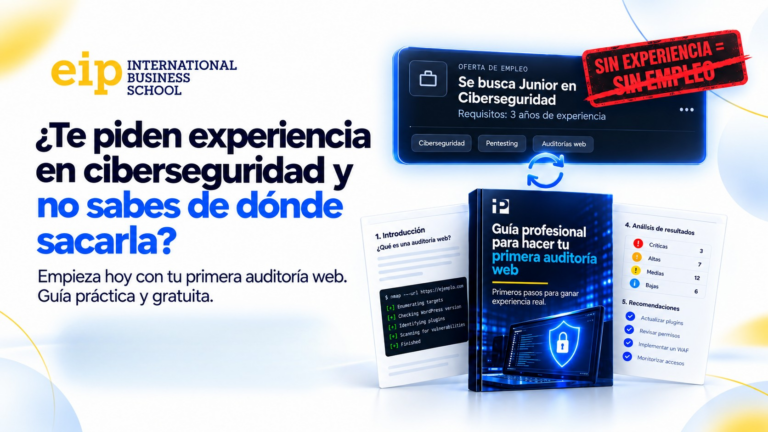
Free resource: Professional guide to performing your first website audit with WPScan. In-house laboratory, step-by-step scanning and sample report.
In this article
- Is it possible to get into cybersecurity without experience?
- What do companies understand by "experience"?«
- 5 ways to gain experience in cybersecurity
- How to document your experience
- Mistakes that undermine credibility
- 30-day plan to get started
- WPScan Free Guide
- Frequent questions
Is it possible to get into cybersecurity without experience?
Yes, with one caveat: "no experience" doesn't mean "no preparation." Someone hiring a junior profile doesn't expect you to have worked on a security team, but they do expect you to demonstrate fundamental knowledge, practical experience, and sound judgment.
The market supports it. According to the ISC2 2025 workforce study, 95% of the professionals surveyed reported at least one skills gap in their team. And in Spain, it is estimated that approximately 30,000 unfilled cybersecurity vacancies, With a clear message from EIP's employability department: training must be practical and real.
What do companies understand by "experience" in cybersecurity
It rarely refers solely to years in a position. A combination of four things is usually taken into account:
- Work experience in a security team or at a nearby technical station.
- Practical projects: laboratories, audits of own environments, tools actually used.
- Training and certifications that validate your theoretical basis.
- Community and continuous learning: CTF challenges, talks, a technical blog.
The last three are within your reach today. And practical projects are the ones that most closely resemble a real workday.
5 ways to gain cybersecurity experience without working in the industry
1. Set up your own testing laboratory
A lab is your own isolated environment where you can practice without risk to anyone: a local website, a deliberately vulnerable virtual machine, or a small test network. It can be set up for free with a standard computer. The golden rule: practice only in your own environments or with explicit written authorization.
2. Do a practical project: your first web audit
The most direct way to gain demonstrable experience is to audit your own lab from start to finish: recognize, list, analyze, report, and remediate. A good starting point is a WordPress site and a tool like WPScan, which identifies exposed versions, plugins, themes, and users and compares them to known vulnerabilities.
The important thing is not to execute the command, but interpret the result and document it: what you have found, what risk it entails and what you propose to do.
Do you want to start today? We've prepared a free guide that takes you from zero to your first audit. Download the WPScan guide.
3. Practice on challenge platforms
Platforms like TryHackMe, Hack The Box wave PortSwigger Web Security Academy They offer environments designed for learning. To understand the most common web vulnerabilities, the reference is the OWASP Top 10. They provide structure, but their challenges are closed: complete them with your own project.
4. Build your foundations and validate them with an entry-level certification
Networking, Linux, HTTP, and basic security concepts are the foundation. To validate these skills, there are initial certifications such as CompTIA Security+ or ISC2 Certified in Cybersecurity (CC). They help you get past a first filter, but they don't replace practice.
5. Participate in the community
The CTF challenges (Capture the FlagMeetups and online groups provide feedback, contacts, and reasons to keep learning. If you're drawn to bug bounty programs, only participate in those with clearly defined rules and scope.
How to document your experience so that it matters
Making plans is not enough: they have to be visible.
- One report per project: scope, findings ordered by severity, evidence and recommendations.
- A simple portfolio: a public repository or a personal page with your lab and your reports.
- A "before and after": the discovery, the correction, and the verification that it has disappeared.
- A clear line in the CV: «"Laboratory project: security audit of a WordPress site with WPScan; report with prioritized findings and verification of fixes.".
Always present them as what they are: laboratory projects, No work experience required. Honesty is noticeable and valued.
Mistakes that undermine credibility
- Scanning without authorization. In Spain, unauthorized access to a computer system can be a crime. Practice only in your lab or with written authorization.
- Publish real third-party data (users, third-party URLs, sensitive screenshots) in your portfolio.
- Inflate your resume. Writing "pentester" after a tutorial is detected in the first technical question.
- Staying on the list of findings without priority, recommendation, or verification.
30-day plan to get started
- Week 1: Review the basics of networking, Linux, and HTTP, and set up your lab.
- Week 2: Install WPScan and scan your lab; save the results.
- Week 3: Order the findings by severity and write your first report.
- Week 4: Correct it, rescan to verify, and publish the project in your portfolio and professional profile.
Free guide to performing your first website audit with WPScan
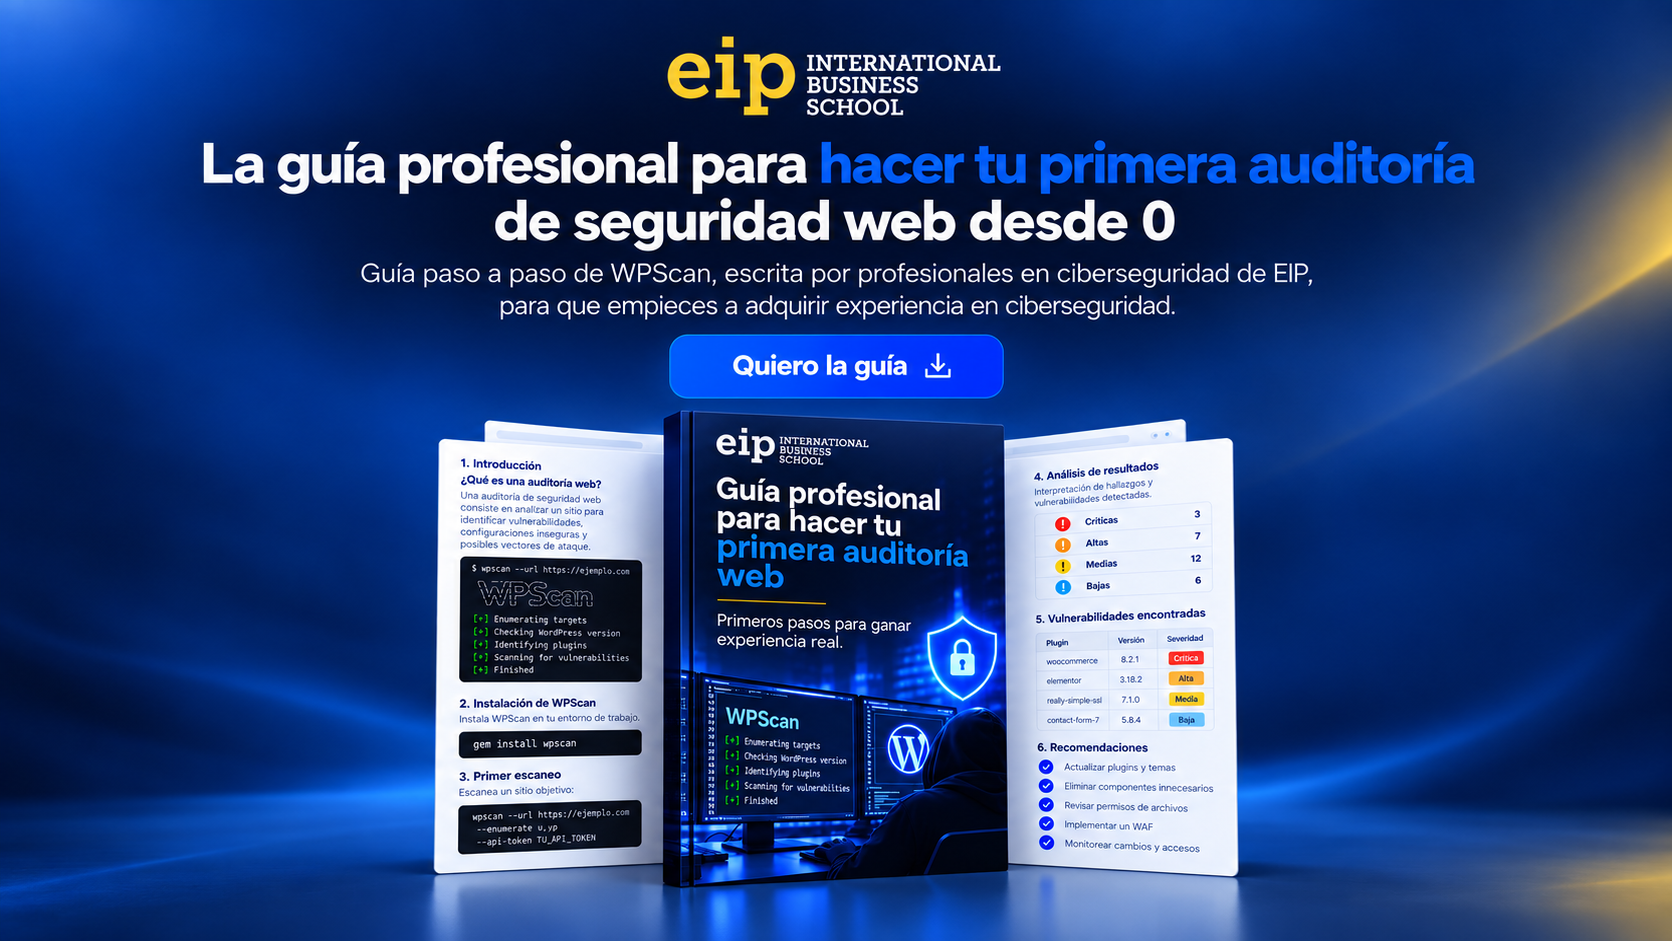
To help you follow this plan without getting lost, we've compiled everything into a guide written by Gonzalo López of EIP International Business School. It's designed for beginners and includes:
- A custom lab with Docker, with the file ready to use.
- WPScan installation step by step and five practical cases.
- How to interpret the results: severity, CVE and priorities.
- A report template and a sample report for your portfolio.
- How to correct each finding and how to verify that it has worked.
It's 32 pages long, free, and in PDF format. You fill out a short form and receive it by email.
Download the free WPScan guide →
Remember: Always use WPScan in your lab or with express authorization. We learn ethically and legally.
Frequently asked questions about gaining experience in cybersecurity
Is it possible to work in cybersecurity without experience?
Yes, although it is common to start with entry-level positions and demonstrate your level with practical projects, training and, if you wish, an initial certification.
What cybersecurity projects can I put on my CV?
A personal lab, an audit of a test WordPress site with its report, challenges solved on practice platforms, and your participation in CTFs. Present these as lab projects.
Do I need certifications to work in cybersecurity?
Not always. An entry-level certification helps validate your foundation, but it doesn't replace practice: it's best to combine both.
Is it legal to practice ethical hacking on my own?
Yes, provided it's done within your own environment or with express written authorization. Scanning third-party systems without permission may constitute a crime. This article is not legal advice: if you have any questions, consult a professional.
And if you want to go further
If after your first project you want to professionalize your profile, at EIP International Business School we offer the Master in Cybersecurity Online training with active professionals and real-world practice. If you'd like to know if it's right for you, an advisor can answer your questions with no obligation.